
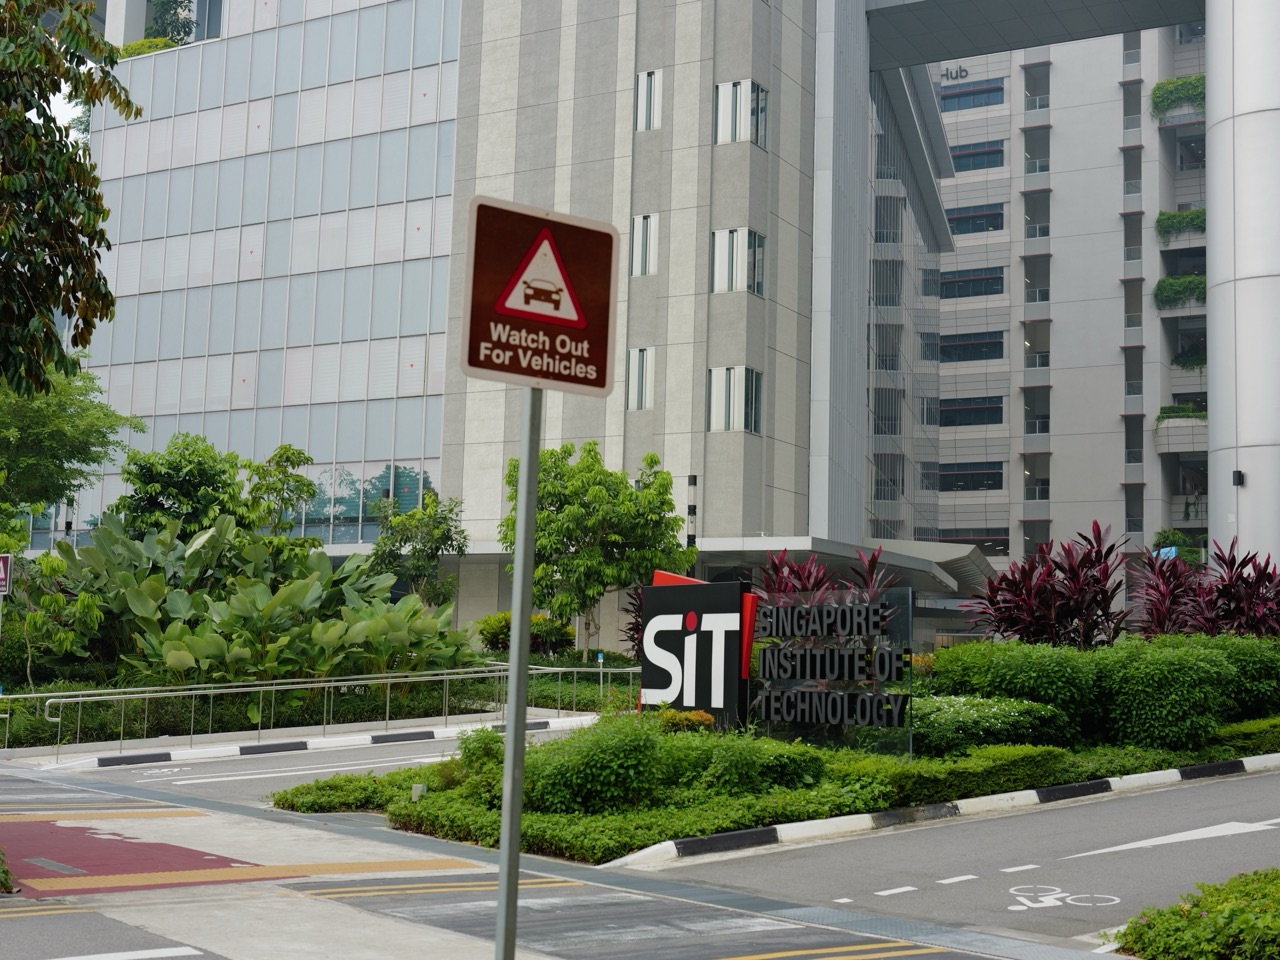
Punggol Digital District is positioned as a Singapore cluster for the digital economy, including cybersecurity, but proximity to banks, technology firms and public agencies does not automatically create a profitable cybersecurity company. For an entrepreneur in Punggol, Sengkang, Pasir Ris or elsewhere in Singapore planning 2027–2037, the business question is which precise security service the firm is qualified and authorised to deliver. A managed security operations centre, penetration-testing service, basic cyber hygiene consultancy and ordinary IT support business have different responsibilities, costs and sometimes different legal obligations. A credible supplier must be able to explain its scope before a customer shares sensitive systems or information.
As of 1 November 2026, the Cyber Security Agency of Singapore identifies penetration testing and managed security operations centre monitoring as the two currently licensable cybersecurity services under its framework. On 2 March 2026 CSA announced that relevant licensed providers must achieve Cyber Trust Mark Level 3, with a grace period extending to 31 December 2026. The consultation closing note confirmed updated conditions and explained that a separate Data Protection Trustmark would not be made mandatory under this review, although data protection obligations remain. JTC includes CSA and the Association of Information Security Professionals among Punggol Digital District’s ecosystem participants. These facts establish a real industrial and regulatory context; they are not promises of contracts for any new vendor.
- Industry cluster: Punggol Digital District and businesses requiring cybersecurity across the North-East and wider Singapore market.
- Distinct service types: Authorised penetration testing, licensed managed SOC monitoring, cyber resilience planning, employee awareness and appropriate implementation support.
- Licensing: CSA currently licenses the defined penetration-testing and managed SOC monitoring service categories.
- 2026 regulatory development: Relevant licensed providers face the Cyber Trust Mark Level 3 requirement, with updated certification and licence conditions.
- Buyers: SMEs, larger enterprises, technology companies and public-sector organisations, each with different procurement and risk requirements.
- Core promise: Deliver a defined security outcome, with sound evidence and escalation arrangements, not perfect immunity from cyber incidents.
- 2027–2037: Business planning horizon, not a guaranteed forecast for cybersecurity revenue or jobs.
- First action: Decide whether the proposed service is licensable and build the required operating capability before accepting work.

What is a cybersecurity service provider?
A cybersecurity service provider helps an organisation manage defined risks affecting its computers, accounts, networks, applications or operational systems. Depending on its business model, it may advise on policy, install or manage security controls, monitor alerts or conduct authorised testing. The scope matters enormously. A person who teaches staff to recognise suspicious emails is not automatically equipped to run a continuous security operations centre. A skilled developer is not automatically authorised to investigate a stranger’s systems.
A professional company describes the service in terms a customer can understand. Which assets are included? What information will be collected? What outcome is expected? When should the customer expect a response? Which decisions remain with the customer? A company that cannot answer these questions should not compensate by using dramatic language about hackers and artificial intelligence. Commercial credibility begins with boundaries.
The Punggol connection and why it is commercially relevant
JTC’s Punggol Digital District includes organisations concerned with technology, finance, government digital services and cybersecurity. That can create a useful regional professional network and potential collaboration opportunities. But a directory of ecosystem participants is not a purchasing list. A startup cannot claim endorsement by JTC, CSA, a bank or an industry association just because they operate in the same district.
The most viable initial customer could be a smaller business in Sengkang or Pasir Ris with an everyday problem: insecure account access, unreliable backups or a lack of a tested incident plan. It could also be an established enterprise elsewhere in Singapore. Location becomes valuable when it improves collaboration or response, but the customer’s actual risk and budget determine the contract. Punggol is a possible business base, not proof of demand.
This article is not an education or career forecast
Our Punggol cybersecurity education guide explains pathways into related knowledge, while our Punggol cyber career overview examines work and skills. This article instead addresses what a business sells, the licensing boundary, the cost of providing reliable service and how procurement decisions are made.
The distinction is important for search relevance. A resident asking how to secure a home account needs practical security advice. A student researching courses needs admissions information. A company founder needs to know whether employees must provide monitoring at night, how liability is allocated and whether the service can survive a slow sales cycle. These are separate questions and deserve separate answers.
The two licensed cybersecurity service categories
CSA states that its licensing regime currently covers two defined service categories: penetration testing and managed security operations centre monitoring. The categories are prioritised in part because providers may encounter sensitive customer information and have significant responsibilities. The applicable definitions matter more than the marketing label chosen by the company. A service described as an assessment, monitoring platform or outsourced security desk may still require evaluation against the official rules.
A founder should consult the Cybersecurity Services Regulation Office when there is uncertainty about the planned activity. It should not assume that having no office in Punggol, offering services online or employing only a few people removes regulatory requirements. Equally, it would be inaccurate to say that every business giving ordinary security advice needs both licences. Match the actual service to the current legal framework.
Managed SOC monitoring is more than buying an alerting tool
A managed security operations centre monitors specified systems or security information, investigates or classifies signals according to its agreement and helps coordinate responses. Software may automatically collect and correlate events, but somebody must decide which events deserve attention and who should act. A supplier offering a real managed SOC service needs suitable systems, trained people, operating procedures and customer communications.
The business must state whether it monitors around the clock, during specified hours or only when an alert is triggered. It must distinguish an automated notification from human investigation. Customers need to know who takes a call at midnight and what happens if the main engineer is unavailable. A supplier that advertises continuous protection but has no realistic staffing arrangement creates a commercial and trust problem.
Penetration testing must be authorised and controlled
Penetration testing assesses weaknesses under an agreed legal and technical scope. A professional provider confirms the customer’s permission, defines which assets and techniques are included, and agrees on emergency contacts and stopping conditions. It must protect sensitive findings. Security testing should never be performed against buildings, networks, devices or websites merely because they are visible from a public place or appear technically reachable.
A good report helps the customer understand risk and remediation priorities. It does not disclose a business’s secrets unnecessarily or exaggerate the significance of every finding. The provider should also explain the limits of the test: a bounded assessment cannot prove that an organisation is permanently secure. Clear method and confidentiality are central parts of the product being sold.
What the 2026 Cyber Trust Mark change means
On 2 March 2026, CSA announced that licensed providers of penetration testing and managed SOC monitoring services would need Cyber Trust Mark Level 3 certification by the end of the year. Its subsequent closing note described the implementation, including the grace period through 31 December 2026. An owner planning business operations from 2027 should check the current requirements for new applications, renewals and active certification.
Certification is not a logo that can be printed merely because a consultant was hired. It requires organisational processes and evidence assessed under the relevant framework. The business may need stronger governance, secure access practices, incident readiness and documented controls. A supplier should budget the necessary time, staff and independent assessment, then verify its status before making claims in sales materials.
Cyber Essentials is not identical to Cyber Trust
CSA’s Cyber Essentials mark supports foundational security practices for organisations. Cyber Trust is designed to address more complex risks through a risk-based framework. The enhanced versions include cloud, operational technology and AI security. Both can be helpful in the marketplace, but they are not interchangeable with a licence to provide a defined regulated cybersecurity service.
A small retailer may use Cyber Essentials as a structured guide to better practice. A highly exposed enterprise may need more advanced assurance. A cybersecurity supplier should be precise when describing its own certification and recommending a customer’s route. It should not imply that installing one product automatically confers certification. The independent assessment process and current criteria matter.
Customer risk must be understood before selecting technology
A restaurant owner with a cloud point-of-sale system may care most about payment disruption and access to online accounts. A manufacturer may worry about production systems. A healthcare supplier may need confidentiality and dependable records. A company managing critical systems has a different regulatory and operational context. The same expensive monitoring product is not necessarily appropriate to every business.
A professional vendor starts by asking which business functions are essential, who can access them, and what realistic failure would cost. It then prioritises safeguards that match the customer’s circumstances. A company that recommends maximum expenditure before understanding the organisation may not be acting as a trusted adviser. A sensible assessment recognises existing controls and explains why each proposed addition is useful.
Incident response must be described in the contract
An alert is only the beginning of the response process. The customer and supplier should decide who may investigate, isolate a compromised system, reset access, communicate with staff or notify relevant parties when required. Some activities may be included in managed monitoring; others may be a separate service needing additional expertise and authorisation. Never assume that a monitoring contract transfers all decision-making authority to the vendor.
A practical response plan includes primary and backup contacts, severity definitions and steps for confirming whether the incident is genuine. It should also consider what happens if normal communication channels are unavailable. A supplier should test the arrangement through approved exercises. The first serious incident is a poor time to discover that nobody knows who can shut down an affected service.
A service-level agreement should measure something meaningful
Some vendors advertise rapid response without stating what the clock measures. Does it mean an automated acknowledgement, an analyst opening the alert, the customer receiving a call or an issue being fully resolved? These are very different promises. A credible SLA defines the starting event, the relevant severity level, the service hours and the provider’s obligations.
The supplier can measure alert acknowledgement, escalation time, reporting completeness and coverage of agreed systems. It should not chase a low average response time by ignoring difficult incidents or closing alerts without review. Customers also need to understand false positives and situations where evidence is insufficient. Trust increases when the vendor reports limitations and mistakes as carefully as successful interventions.
Staffing is the hidden cost of an always-on security business
A company promising round-the-clock monitoring must consider shifts, supervision, leave, training and technical escalation. One person watching messages after office hours is not a durable operating model. Automation may reduce repetitive work, but human expertise remains necessary for unusual events and judgment calls. The founder should calculate staff coverage before quoting a monthly service fee.
Imagine an illustrative managed service receiving S$25,000 in monthly recurring revenue. If qualified staffing costs S$14,000, technology and hosting S$4,000, administration S$2,000 and compliance provisions S$2,000, the remaining contribution is S$3,000 before other expenses and tax. These figures are hypothetical, not Singapore market rates. If the firm must add another staffed shift, the contract may become unprofitable. Pricing must reflect actual coverage.
Security tools create their own operating responsibilities
A managed service may depend on log collectors, cloud platforms, endpoint tools, ticketing systems and communication channels. These require maintenance, access control and a plan for outages. A vendor should not assume that buying subscriptions completes the service. It needs to know what happens when a monitored device stops sending information or when the monitoring platform itself is unavailable.
Customers should receive evidence of coverage limits. An empty dashboard can mean that nothing suspicious happened, but it can also mean that data collection failed. The provider should detect and report such gaps. Accurate system inventories and change management are therefore part of the business. A company that maintains data quality well may provide greater value than one displaying complex visualisations without verifying its inputs.
The supplier’s own cybersecurity is a business risk
Security providers can hold privileged access and confidential data from many customers. An incident affecting the vendor may therefore affect several organisations. The company needs strong internal access control, appropriate staff screening, secure record handling, independent oversight where necessary and a reliable exit process when employees leave. Clients should know who can see their information and how long it will be retained.
CSA’s 2026 consultation closing note emphasised data protection responsibilities while declining to make the separate Data Protection Trustmark mandatory for licensed providers under that revision. This should not be misinterpreted as permission to disregard personal-data law or client confidentiality. A new vendor needs to protect information as part of its ordinary operations, not wait until an audit requires documents.
Cyber hygiene may be the most useful first service for an SME
Many small companies lack a dedicated security department. Basic account protection, software updating, careful backups and employee awareness can reduce avoidable risks. CSA’s Cyber Essentials resources and toolkits offer structured guidance. An advisory firm may help a business assess where it stands and document a reasonable improvement plan, within the scope of its actual competence.
The service provider should not use fear to sell a large subscription. If the customer can make a substantial improvement with well-configured existing tools, explain that. A business model based on honest advice can produce lasting relationships. A firm that pushes advanced monitoring onto an organisation without the systems or budget to use it effectively may create more expense than protection.
Training employees without pretending every message is malicious
An employee awareness service can help staff recognise suspicious requests, verify unusual instructions and report concerns. The best programme treats employees as part of a responsible organisation, not as people to embarrass. Content should fit the business’s actual workflows. A retail team handling deliveries faces different scenarios from a finance department approving transfers.
The provider can measure whether participants understand reporting routes and how confidently they can verify a request. Avoid collecting excessive personal information about employees or publishing names of people who made mistakes. Simulated exercises should be approved and carried out under clear rules. The commercial outcome is better readiness and communication, not a competition to identify a single careless individual.
Cloud security is not the same as on-premises security
A company using cloud services may need to manage identities, permissions, configurations, data storage, application secrets and relationships with external providers. Some responsibility belongs to the cloud vendor and some remains with the customer under the applicable service arrangement. A security supplier must understand that division before promising to protect the environment.
A narrow cloud review can identify permitted configuration improvements and help the client establish an inventory of important services. The vendor should be careful about privileged access, customer data and changes that could interrupt business operations. If it offers continuous monitoring, that may bring additional service scope and licensing questions. Good security work begins with an agreed set of tasks and a safe change process.
Operational technology requires specialist boundaries
Connected buildings and industrial installations may use operational technology to manage physical equipment. A fault or unauthorised change can have safety consequences beyond an ordinary office IT incident. A general security consultant should not perform intrusive tests on live engineering systems without the necessary authorisation, qualifications and operational controls. The owner or operator must remain involved.
Punggol Digital District’s energy and building systems make this a relevant topic, but they are not open infrastructure for public experimentation. A business can learn from simulated environments or authorised projects before attempting specialist work. The supplier should distinguish monitoring and documentation from live control. The ability to explain what must not be touched is a valuable part of professional competence.
AI security creates opportunities and new liability questions
Organisations increasingly deploy AI-assisted tools for writing, coding, support and process automation. Those systems can create risks involving confidential information, excessive permissions, unreliable outputs and insufficient review. CSA’s enhanced certification materials include AI security as a relevant domain. A provider may help a business evaluate vendors, define acceptable use and establish human oversight.
But AI systems are not all alike. A vendor should not claim that one generic assessment certifies every model or guarantees safety. It must understand the actual use case, the data involved and the impact of an incorrect response. A startup offering AI-security advice should disclose its own expertise and test methods. The customer needs practical controls, not a fashionable label that hides unresolved decisions.
Vendor and supply-chain risk are a separate service niche
A business may secure its own laptops and still be vulnerable to a poorly managed contractor or cloud service. Suppliers can have access to accounts, customer records or operational systems. A cybersecurity consultant may help the organisation map those dependencies, define security expectations and plan how access is removed when contracts end.
A questionnaire can be useful, but it does not by itself establish that a supplier is safe. Reviews should prioritise critical providers and consider actual evidence. A small Punggol firm might specialise in helping SMEs maintain simple supplier inventories and clear access procedures, provided its service is accurate and within scope. This is a practical business function that can have value even without a dramatic threat simulation.
How a small vendor should qualify for larger contracts
Larger customers may require proof of business registration, relevant CSA licences, genuine certifications, appropriate insurance, audited processes, staff competence and financial stability. They may also ask about business continuity, privacy and subcontractors. A founder should prepare truthful evidence before submitting a tender. Association membership or a Punggol Digital District office address cannot replace those requirements.
A one-page capability statement should explain services, coverage, exclusions and who is accountable. Relevant project references can help, but confidential customers should not be named without permission. If a buyer requires a qualification the firm lacks, the company may develop that capability, partner appropriately or decline the contract. It should never fabricate status to win an evaluation.
The cash-flow problem behind long enterprise procurement cycles
A supplier may spend months preparing proposals, completing assessments and answering vendor-risk questions before revenue begins. Meanwhile, engineers require salaries and tools have recurring subscription costs. A founder should estimate how much working capital is needed while waiting for contracts. A technically strong firm can fail if it assumes every promising meeting produces a purchase order next month.
The owner should separate likely opportunities from confirmed revenue and use conservative conversion assumptions. It can pursue smaller appropriately scoped customers while preparing for larger accounts. The business also needs a plan for annual renewals and potential contract termination. Revenue concentration is dangerous when one customer supports most of the team. A diversified but manageable portfolio may be more resilient.
A fictional Punggol retail-security customer
Imagine a Punggol retailer operating an online store, cloud inventory system and several employee devices. It asks for better protection after receiving suspicious account messages. An adviser begins with a bounded review of account management, backups, software maintenance and staff reporting procedures, without conducting unapproved penetration testing. The customer receives a plain-language list of priorities and a record of which actions it has authorised.
The engagement is commercially useful because the deliverable is understandable and the cost can be estimated. It does not promise that a cyberattack will never happen. If the customer later needs regulated monitoring or penetration testing, the supplier must ensure that the work is carried out by an appropriately licensed provider. Honest scope boundaries protect both businesses.
A fictional managed SOC proposal for a larger organisation
A larger company asks for continuous monitoring of designated systems. The proposed supplier explains which log sources are included, how alerts are classified, when staff are available and what incident escalation entails. It provides actual licensing and certification details and shows how customer information is protected. The buyer also wants assurance that the provider can continue operating during a platform outage or employee absence.
Before accepting, the supplier calculates the full staffing and technical cost. It tests its escalation process with the client and documents limitations. A clear monthly agreement may be more valuable than a complex dashboard demonstration. If the customer expects additional investigations or recovery work, those responsibilities should be priced and defined rather than silently assumed.
A fictional cybersecurity training provider
A small training firm has experience explaining cyber hygiene to nontechnical staff. It develops workshops with realistic scenarios for shop owners, office managers and front-line workers. It avoids claiming that course completion certifies an organisation under CSA’s programmes. Where participants need a formal certification route, the provider points them to the applicable official framework and appointed certification bodies.
The firm charges for defined sessions, materials and follow-up support. It measures whether employees know what to do when a suspicious message arrives. If the programme requires personal or sensitive organisational information, it establishes proper handling conditions. The business grows through repeat usefulness, not through a promise to eliminate every cyber threat in one afternoon.
2027–2029: establish permission, maturity and repeatable service
In the near-term period, firms offering licensed services should begin by confirming that their regulatory and certification requirements are satisfied after the end-2026 transition. Other security businesses should also use appropriate controls and accurately describe their services. Customer needs may expand as organisations become more digital, but demand will differ by sector and budget.
A small vendor should aim for a few well-scoped engagements, documented results and dependable customer support. It should not stake its entire business on obtaining one major Punggol Digital District tenant. A customer outside the district can be equally valuable. The first three years should show whether the firm can protect information, fulfil service levels and maintain a sensible margin under normal conditions.
2030–2033: make systems and staff more resilient
If the company has recurring revenue, it may expand into new technical environments or support additional customers. Before doing so, the owner should review which capabilities genuinely transfer. A monitoring process suitable for small cloud accounts may not be safe for industrial control networks or highly regulated data. Additional expertise, training and agreements may be necessary.
The business should establish knowledge transfer so that one analyst’s departure does not compromise a customer. It needs tested procedures for platform changes, subcontractors and incidents affecting its own systems. Profitability should be evaluated after staffing, audit and support costs rather than by headline contract value alone. The dates are scenario checkpoints, not official promises about cybersecurity industry growth.
2034–2037: trust becomes the durable product
By the end of the decade, tools and threats will have changed. A vendor that depends entirely on one software product or on one individual expert may struggle when customers migrate to a different platform. The firm should retain the ability to understand risk, document decisions and communicate clearly even as technical systems evolve.
A trustworthy provider admits limits, corrects errors and protects client information when a relationship ends. It can adapt pricing and staffing as customers grow, and it does not make impossible claims of total protection. The future of cybersecurity business is uncertain, but responsible service remains a defensible principle across many technologies. The organisation’s reputation is built from what it actually does, not the list of acronyms on its website.
Checklist for a new cybersecurity business
- What exact service is offered and what activities are excluded?
- Does the service fall within CSA’s current licensing categories?
- What certification and licence conditions apply after the 2026 changes?
- Who owns the customer systems and authorises every activity?
- Which information may staff view, copy or retain?
- Are service hours, response targets and escalation responsibilities explicit?
- What happens when the provider’s own monitoring or communication fails?
- Can the workforce meet the promised service level during leave and emergencies?
- How are customer credentials and confidential findings protected?
- Are certifications, experience and references accurate and current?
- What does the customer receive as evidence of actual improvement?
- Has the business calculated qualification and recurring operating costs?
- What happens when the contract ends or the customer changes technology?
- Which work should be referred to a more qualified or licensed provider?
The checklist makes the business more credible because it distinguishes lawful competence from enthusiasm. A founder who does not yet have every answer can develop the capability before taking responsibility for someone else’s sensitive systems. That is a stronger foundation than winning a contract with vague promises.
Frequently asked questions
Does every IT consultant require a CSA cybersecurity service licence?
No. CSA identifies two defined licensable categories at present: penetration testing and managed SOC monitoring. Businesses must assess the actual activity against the current legal definitions. Ordinary IT support should not be automatically described as licensed penetration testing.
Does Cyber Trust Mark certification make a business immune from attacks?
No. Certification demonstrates conformity with relevant requirements within its scope and does not guarantee a zero-incident future. Security controls and staff practices need continuing review.
Can a firm test a Punggol Digital District system just because it is nearby?
No. Technical testing requires the system owner’s authorisation and applicable legal compliance. Public location does not make a network or operational system open for testing.
Is buying security monitoring software the same as providing a managed SOC?
No. A managed SOC service includes defined monitoring, staffing and escalation responsibilities. A standalone tool may be one component but does not automatically satisfy the supplier’s contractual or regulatory obligations.
Is Cyber Essentials the same as the Cyber Trust requirement for licensed providers?
No. CSA publishes distinct certification schemes. The March 2026 announcement and subsequent conditions specifically address Cyber Trust Mark Level 3 for the relevant licensed service providers. Verify the latest wording directly.
Are cybersecurity profits guaranteed through 2037?
No. Demand for security does not guarantee any vendor’s revenue. Licensing, staffing, product fit, competition, technical quality and customer trust determine whether a business is viable.
Your Next Step: build one defensible service rather than a security slogan
Choose a problem you understand, determine whether the planned service requires CSA licensing, and write a scope a customer can verify. Build the internal controls, staff coverage and incident procedures before making strong promises. Show how the service makes the customer’s operations more resilient, including its limitations and cost. If the buyer needs capabilities outside your competence, use a legitimate specialist partner or decline the work. The industry rewards trust earned through behaviour, not proximity to a technology hub.
Official sources: JTC’s Punggol Digital District business ecosystem, CSA’s Cybersecurity Act overview, CSA’s March 2026 Cyber Trust Mark announcement, CSA’s service-provider licensing consultation closing note, CSA’s Cyber Essentials certification guide, CSA’s Cyber Trust Mark certification guide and CSA’s October 2026 enterprise security statement. Confirm current requirements with the relevant authority and customer before commencing regulated service.


