
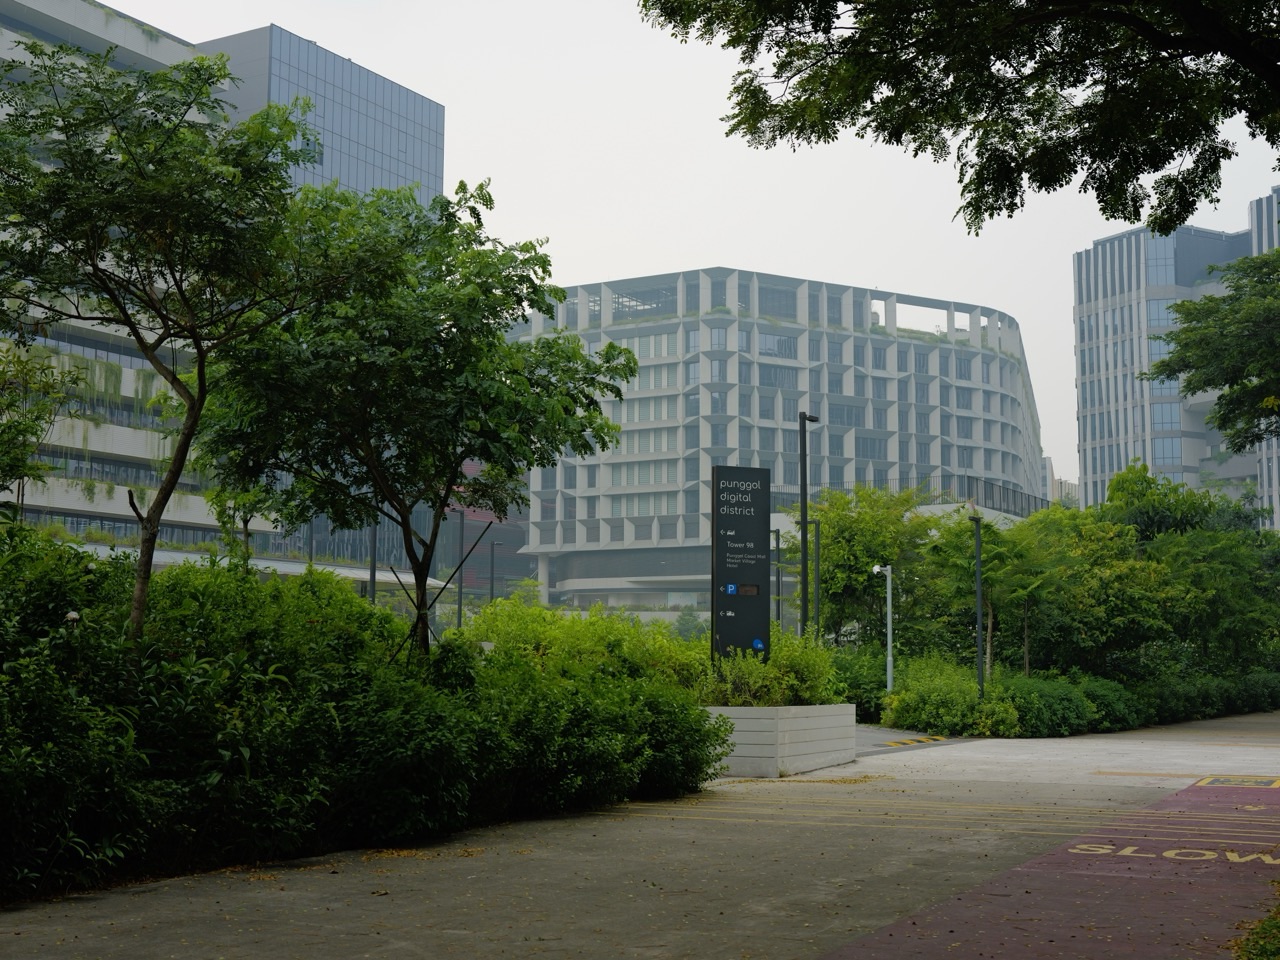
What is scheduled at GovTech in Punggol
Quick answer, checked 23 October 2026. The GovTech Digital4Good Online Safety Hackathon is advertised for Friday, 6 November 2026, 11 am–7 pm at GovTech, Punggol Digital District, 82 Punggol Way, Singapore 829910. The organisers’ event page says it brings together students, mentors and public officers to explore practical ways to make digital spaces safer. It names four broad challenge directions: Trust, Commerce & Fraud; Gen AI Deception; Technology-Enabled Harms; and Gen AI for Good.
Importantly, the Luma registration page explicitly states approval required: registering is a request to join, not a guaranteed admission. Its public description welcomes people new to hackathons, but it does not provide a blanket guarantee that every age group, student or walk-in visitor will be accepted. The event time is also shown by an external events collection referencing the same organiser link; interested participants should use their accepted confirmation for definitive arrival instructions.
This Punggol event is distinct from a general lecture on cybersecurity or the CSA Minecraft workshops also scheduled in November. A hackathon asks participants to frame a problem, build or communicate a prototype and consider whether it helps real users. The educational value lies in critical reading, ethical design, teamwork and responsible evaluation, not in promising a functioning production app after one day.
Confirmed information and what is still an open question
Title: GovTech Digital4Good Online Safety Hackathon. Date: 6 November 2026. Advertised time: 11 am–7 pm Singapore time in the external calendar listing. Location: GovTech at Punggol Digital District, 82 Punggol Way. Registration: approval required through the organiser’s Luma page. Named supporting community partners: IMDA Digital for Life, GovTech, Kebun Baru and SMU AI Club in the public description.
The listing does not establish a particular participation fee, eligibility for every minor, a guaranteed mentoring session, a prize structure, equipment provision, meals or a precise internal room. These are details to clarify with organisers. ’80 going’ on a public event page is not an authoritative statement about current vacancies or a reservation for a new registrant.
Participants should keep the accepted invitation, check any ID or security requirements and arrive at the location communicated by hosts. GovTech premises are workplaces, not unrestricted public exhibit space. A digital district address is not enough to presume permission to enter every building.
What is a hackathon, and what is it not?
A hackathon is a time-bounded collaborative event in which people work on defined problems and explore possible solutions, often through software, prototypes, research or demonstrations. The term ‘hack’ in this setting describes constructive experimentation; it does not grant permission to access other people’s accounts, exploit real websites or collect private data without authority. This difference should be explained clearly to first-time participants and families.
A good educational hackathon values clarity of problem definition and thoughtful validation. A participant may create a storyboard or simple prototype that explains a safe reporting process, then test whether the intended user understands it. That may be more responsible than hurriedly deploying a complex system that cannot be evaluated for privacy, accuracy or safety.
A one-day event is not an accredited computer-security course, an official government recruitment exercise or a promise that GovTech will deploy an idea. Projects need later testing, permissions and professional review before any real-world use.
Why this event matters to Punggol’s education future
Punggol Digital District was developed by JTC as an ecosystem linking education, business, public-sector technology and community. GovTech’s presence makes public digital services and their safety a visible part of the local work environment. An event at the district can give students a concrete context for learning why trust and usability matter in technology that people rely on.
That setting is not proof that every Punggol school pupil gets privileged access to government systems or that the hackathon forms part of an MOE examination syllabus. Participants still have to follow event eligibility and permissions. The opportunity is to encounter professionals and useful problem statements that can inspire later study and thoughtful careers.
This story therefore focuses on a named 6 November event and its decisions. Wider eduKatePunggol guides can explain cybersecurity and career pathways separately without repeating the same general content under a new headline.
Challenge one: Trust, Commerce and Fraud
The organiser invites ideas for making online transactions safer, reducing scams and detecting fraud. These are problems involving people, behaviour, payments, information and verification. A strong hackathon entry should begin with a narrowly defined user: for example, a first-time online shopper who struggles to decide whether a payment request is genuine. The team should identify the user’s actual difficulty before designing alerts.
A bad solution could create more danger than it prevents. An app asking users to upload bank passwords to ‘verify scams’ would be inappropriate. A prototype built from fictional messages, with clear instructions to use official sources, can demonstrate safer reasoning. If a system claims it can detect fraud automatically, it must explain its uncertainty and how users can confirm important decisions independently.
The learner’s transferable skills include checking evidence, writing precise prompts, distinguishing a trustworthy source from an attractive interface and recognising that security measures must fit ordinary users rather than shame them.
Challenge two: Gen AI Deception
The public problem description names deepfakes, synthetic voices and other AI-generated deception. As generative tools improve, realistic-looking content cannot by itself authenticate a speaker’s identity or a message’s claims. The relevant lesson is source verification and trustworthy communication rather than a belief that every unfamiliar image is fabricated.
A student team might design a fictional decision guide that helps users ask: Who published this material? Can the claim be independently confirmed? Is the message pressuring me to share a secret or make an immediate payment? Is a trusted channel available? The prototype should avoid turning a tentative suspicion into an accusation against a real individual.
Automated detection also has limits. A tool may flag genuine content incorrectly and fail to flag some manipulated content. If teams include AI in a design, they should report false positives, false negatives, uncertainty and privacy implications instead of promising flawless results.
Challenge three: Technology-Enabled Harms
The organisers include cyberbullying, doxxing, harassment and non-consensual sharing among possible topics. These involve real people and can carry serious emotional and privacy consequences. A thoughtful hackathon design puts affected users’ safety first and avoids requiring them to disclose more sensitive content than is necessary for help.
One safe project idea is to prototype a reporting flow using fictional material: who can seek help, what information should be provided and how a user can understand the next step. A reporting interface is not useful merely because it has a button. The team must consider whether victims understand the instructions, whether the process exposes them to further harm and whether the organisation has an appropriate response capability.
Participants should never create or distribute abusive examples involving real people to demonstrate a feature. Use invented names and benign placeholder content; follow organisers’ rules and respect the privacy of other participants.
Challenge four: Gen AI for Good
The event also invites thoughtful uses of AI to support wellbeing, community safety and digital confidence. A socially valuable idea might help a user find trustworthy digital-safety information in an accessible form, but the team must check whether the system’s answers are accurate and whether sensitive information is retained or exposed.
The label ‘for good’ cannot substitute for evaluation. A tool that generates fluent but inaccurate safety instructions might increase risk. A responsible prototype limits its scope, links to authoritative sources where appropriate, and makes it clear when a human or official service should be consulted.
This is a useful educational lesson about AI: capability is not the same as reliability. The most effective design is often narrower than the most impressive pitch, because it can state exactly what has been tested and what remains unknown.
How to choose a problem without duplicating everyone else’s idea
A team should start with a specific problem statement in one sentence. ‘Make the internet safer’ is too broad to guide a one-day project. ‘Help a new online shopper verify an unexpected payment demand through established official channels’ is narrower and leads to testable design choices. The next question is what observable result would show that the prototype helps.
A useful selection method compares impact, ethical risk, time available and access to legitimate information. Projects requiring private case files or live financial data may be unsuitable. Public educational resources and synthetic scenarios can be enough to explore a mechanism without collecting real secrets.
The aim is not to claim ownership of a problem simply because the team has named it. Similar ideas may exist; the team can improve clarity by defining its audience, constraints and validation plan.
A good one-day prototype is intentionally limited
A full digital service needs user research, security architecture, testing, incident handling and ongoing support. A hackathon prototype can demonstrate a narrower interaction and acknowledge the gap. For example, a mock scam-message verification screen might show how a user compares an unfamiliar message with a known official channel. It should not imply the prototype has access to bank systems or provides regulated advice.
A design can be presented as a paper storyboard, a clickable mock-up or simple code depending on the team’s skills and event rules. The organiser has not promised that all accepted participants will have identical technical facilities, so teams should prepare adaptable plans and confirm equipment arrangements.
Resisting overbuilding is a professional habit. A clear explanation with honest limitations is more useful than deploying an untested app just to say it went live.
Define success using real user behaviour, not decoration
Suppose a fictional prototype teaches people to identify when a digital payment request should be independently checked. What evidence would demonstrate improvement? A safe test could ask volunteers to answer questions about invented messages before and after using the prototype, while collecting only information appropriate and authorised for the exercise.
The team should avoid claiming broad effectiveness from a handful of responses. A small sample can reveal whether instructions are confusing; it does not establish that the system will reduce national scam losses. Good measurement considers both positive responses and unintended errors.
A polished graphic, confident pitch or complex model is not a substitute for explaining how the solution changes a user’s decision. The design must be judged against the actual problem it aims to address.
Worked example: a simplified false-alarm calculation
Imagine an invented set of 100 messages, of which 20 are actually malicious. A prototype flags 25 messages for review. Suppose 15 of the flagged messages were truly malicious and 10 were legitimate. In this simplified dataset, the share of flagged messages that are malicious is 15 ÷ 25 = 60%. But five malicious messages were not flagged.
The example exposes an important trade-off. Some users could be unnecessarily interrupted by false alarms, while others might be missed. Reporting only the 60% figure would conceal the missed threats. A careful evaluation would also consider what proportion of actual threats was detected and how cases were labelled.
These numbers are fictional Mathematics practice, not an effectiveness estimate for a real GovTech system or the 6 November event. Their purpose is to show that trustworthy evaluation needs the full comparison table.
Worked example: how sample size affects confidence
A team tests its fictional design with five volunteers, and all five understand the instructions. It may be tempting to claim 100% usability, but five people are too few and may not represent the wider population. A sixth user with different needs may encounter a problem that the first group never saw.
This does not make a small pilot useless. It can reveal clear faults and inspire a better design. The team should report the test group, conditions, questions asked and limitations. Good science distinguishes a small exploratory observation from a robust population-level conclusion.
Secondary Mathematics and Science lessons can prepare students for this reasoning long before they study formal statistical inference. The foundational habit is to ask what the evidence can legitimately support.
Privacy by design starts before coding
An online-safety prototype can become unsafe if it collects sensitive messages, identification documents or private account details unnecessarily. The first question should be whether the service needs the information at all. If synthetic examples achieve the educational purpose, collecting real personal data is often unnecessary for a short event.
Participants should follow organiser and host instructions for devices, data handling and public demonstration. Never upload confidential government, school or employer material into an unapproved AI tool. Do not publish the faces, names or contact details of other attendees without the relevant permission.
The paradox of an online-safety project is that it can undermine user trust while attempting to protect it. Thinking about data minimisation early helps teams avoid that contradiction.
Cybersecurity is more than penetration testing
Students sometimes interpret a hacking event as a chance to attack any nearby system. The Digital4Good event is framed around constructive online safety, and its announcement does not grant permission to test GovTech’s networks, other attendees’ devices or any external service. All technical work must remain within explicit event rules and authorised environments.
Defensive software, education, accessible reporting, human-centred design and risk evaluation can be legitimate ways to contribute without running intrusive tests. Teams unsure about boundaries should ask their mentors or hosts instead of making assumptions.
Professional cybersecurity practice includes legal and ethical responsibility. Understanding those limits is as important as writing code that performs an impressive demonstration.
How mentors can help without taking over
Mentors and public officers are identified as part of the intended hackathon community. The exact mentoring allocations and session format are not published as guaranteed individual entitlements. Participants can nevertheless prepare questions that make professional discussion useful: What user need is this solving? What evidence would show success? What could go wrong? What should be left out of an early prototype?
A mentor’s role is not necessarily to provide code or decide the product for students. Good feedback can challenge weak assumptions and suggest a safer test. A learner should be willing to revise the project if a proposed feature creates privacy risks or exceeds the time available.
Teams should document changes made after feedback and distinguish an expert’s suggestion from a confirmed organiser requirement. This prevents misunderstandings in a fast-moving event.
A role for students who are not strong coders
A team needs more than software programming. Some participants can explain the problem, research official source material, sketch an accessible interface, write user instructions, test comprehension or present evidence. A student who listens carefully to potential users may prevent a technically elaborate but confusing design.
The event’s public description welcomes people new to hackathons, but actual admission remains approval-based. A school pupil should check eligibility with the host rather than assume an open walk-in format. If admitted, the pupil can prepare a small explanation of an issue they care about, without pretending to possess expert competence.
Clear writing, critical reading and Mathematics are genuine contributions to technology projects. They help teams communicate intentions and evaluate claims instead of focusing solely on programming speed.
How Punggol Secondary students can use the themes
A Secondary 1–2 learner can connect the topics to English comprehension and source analysis: who says a message is genuine, what evidence is offered and what information is missing? Mathematics helps with percentages, graphs and the consequences of false alarms. Science supports testing under defined conditions. Computing and CCE or cyber-wellness learning connect algorithms with responsible behaviour.
The 6 November hackathon is not an MOE syllabus announcement or automatic co-curricular activity. School subject combinations and future examination requirements remain governed by the relevant school and ministry. This event provides one optional real-world context for the underlying skills.
An educator can use fictional screenshots and role-play rather than risky real links, and should never require pupils to disclose personal experiences of online harm publicly.
A paper prototype for parents and children
Choose a harmless fictional message: ‘Your parcel has been delayed. Enter a password at the linked page to fix delivery.’ Ask the child to underline the requested action, circle the claimed authority and describe a safer next step. A parent can explain why the child should ask a trusted adult and use the delivery organisation’s established channel rather than the unfamiliar link.
Turn the process into three paper screens: message received, questions to check, and safe next step. Then ask another person to follow the screens without extra explanation. If they become confused, revise the wording rather than blaming the reader.
This is an independent family-learning exercise, not the hackathon’s official problem statement or a guarantee that a child should independently evaluate suspicious links.
A full-day event requires an actual plan
The external events listing gives Friday 6 November, 11 am–7 pm. That is a substantial window for a student or working adult. Ask hosts about arrival time, meal arrangements, accessibility, equipment, age and supervision rules, and whether participants may leave before the programme ends. Those practical details cannot be filled in from assumptions.
The registered location is GovTech at 82 Punggol Way, but exact internal check-in procedures should come from the accepted event confirmation. A public street address does not resolve building security or entry conditions. People who are not approved should not travel expecting access.
For younger participants, parents should obtain explicit organiser guidance about guardian consent or supervision. The public listing does not provide a universal minor-participation rule.
What participants should take away
A good outcome from a hackathon is not necessarily a working commercial application. A student might develop a clearer understanding of fraud risks, learn how to test an interface or discover why privacy must be planned before development. They might also learn that a proposed solution cannot work without reliable data, legal authority or a process for human support.
Encourage participants to record one design decision, one piece of feedback and one question that remains unresolved. An honest list of limitations is valuable, especially where people may rely on the tool for safety. Technical curiosity should increase responsibility rather than overconfidence.
Later study can build on these foundations through authorised school projects, computing modules or professional training; none are guaranteed by event attendance.
A clear follow-up record after 6 November
Following the event, teams can describe the prototype’s purpose, data sources, actual tests, limitations and next steps. If a model was demonstrated with synthetic messages, that should be stated explicitly. Do not exaggerate a mock-up into a deployed government service or describe a mentor’s casual comment as an institutional endorsement.
A student can use the reflection in a portfolio, subject to event rules and permission to include project material. Portfolios should not contain other people’s sensitive information or proprietary assets. Clear responsibility and documentation matter more than inflated claims about adoption.
For parents, a short discussion is enough: ‘Who were you trying to help, and how did you know your design helped them?’ This bridges the one-day event and durable learning.
How this differs from the CSA Minecraft workshops
The separate CSA Minecraft cyber-safety workshops are age-targeted introductory educational programmes on 4 and 24 November with their own requirements. The Digital4Good Online Safety Hackathon on 6 November has a different organiser, venue, approval-based registration and problem-design format.
A family should not confuse one event’s device provision, eligibility or fee with another’s. The fact that both involve cybersecurity and Punggol Digital District does not make their arrangements interchangeable. Choosing responsibly means matching the participant’s interests and ability to the specific organiser’s instructions.
The broader eduKatePunggol cybersecurity youth-pathways guide offers context for learners who want to investigate longer-term study without relying on one event.
Frequently asked questions
What is the event? A GovTech Digital4Good hackathon on online safety at Punggol Digital District. When? Friday 6 November 2026, advertised 11 am–7 pm. Where? GovTech, 82 Punggol Way. How do I register? The official Luma event page has a request-to-join procedure and requires host approval.
Can anyone walk in? The public registration explicitly requires approval, so walk-in access must not be assumed. Does it cost money? The publicly reviewed organiser page does not establish a specific fee or promised free ticket; check the registration conditions. Can schoolchildren attend? The event describes students as part of the audience but does not settle every age or guardian requirement. Seek confirmation before applying.
Will GovTech deploy a winning idea? No deployment promise appears in the public listing. Will participants get prizes or certificates? Such outcomes are not established by the reviewed event page. Ask hosts for the actual programme rules.
A simple threat-model question before building
Every digital safety concept should identify what is being protected, from whom and against which plausible harm. A fictional shopper-verification tool might protect a user from giving information to an impersonator. But it could also create a new risk if the prototype stores private messages unnecessarily. A team can draw a small boundary diagram showing users, information, trusted services and unknown actors. This is introductory thinking, not a substitute for a professional threat model or permission to investigate real people’s accounts. It helps students avoid adding features without understanding their consequences.
Accessibility must be part of the first design
Online safety information helps only when intended users can understand and act on it. An interface that relies on tiny text, colour alone or unexplained jargon may exclude people it is supposed to protect. A team can test a fictional design using simple language, clear labels and multiple ways to understand an instruction. Real accessibility evaluation is more demanding, but early attention can reveal obvious confusion. Avoid claiming the prototype is universally accessible after trying it with only one teammate. Instead, identify its limitations and what further testing would require.
When automated advice should lead to a human
A system that encounters a high-stakes or ambiguous situation should not invent certainty merely to appear helpful. An online-safety prototype may need to tell users when information is insufficient and direct them to an established trusted channel or appropriately qualified support. Designers should not imply that a hackathon project can handle emergency, legal or financial issues without safeguards. Showing a clear boundary around the prototype’s competence can be an indicator of mature engineering judgment. The purpose is to support safer decisions, not replace institutions with a polished but unverified chatbot.
Responsible evaluation of AI-generated explanations
A generative model may produce a fluent response that cites a non-existent rule or overlooks an important exception. Teams can test a prototype using invented examples with independently known correct answers and record both successes and failures. They should distinguish helpful phrasing from factual accuracy. A student who finds an error should document it rather than quietly remove it from the demonstration. Reliable technology development depends on recognising limitations and making corrective decisions, not presenting a curated collection of only successful outputs.
Cultural and language differences affect trust
Digital notices are read by people with varied languages, ages and experiences. A safety message that is obvious to one participant may be confusing to another. Designers can therefore ask how instructions are phrased, whether examples depend on cultural assumptions and what a user should do if unsure. Translation needs checking because a fluent sentence can still distort important meaning. A small hackathon project cannot validate every audience, but it can state whom it is intended to help and which populations would need further review.
A clear post-event claim is a limited claim
After the hackathon, an accurate reflection might say: ‘Our team built a mock-up for verifying fictional payment messages and tested whether a small group could understand the steps.’ It would be misleading to say the system prevented actual fraud unless such an outcome were measured under appropriate conditions. Students should distinguish a concept, prototype, pilot and deployed service. This source-checking discipline protects users and helps prospective employers or educators understand what the participant genuinely contributed.
Official organiser references and additional reading
- GovTech Digital4Good Online Safety Hackathon — organiser-hosted Luma page
- Event listing — Friday 6 November 2026, 11 am–7 pm, GovTech PDD
- JTC — Punggol Digital District context
- IMDA Digital for Life — digital inclusion and confidence
- eduKatePunggol — cybersecurity, trusted sources and digital safety
- eduKatePunggol — CSA Minecraft workshops for school students
Editorial check: 23 October 2026. Event topic, address and approval-based registration derive from the organiser-hosted listing. The advertised 11 am–7 pm date/time is independently shown by the linked event collection. All numerical examples and suggested prototypes are fictional educational exercises, not official hackathon tasks or deployment advice.


