
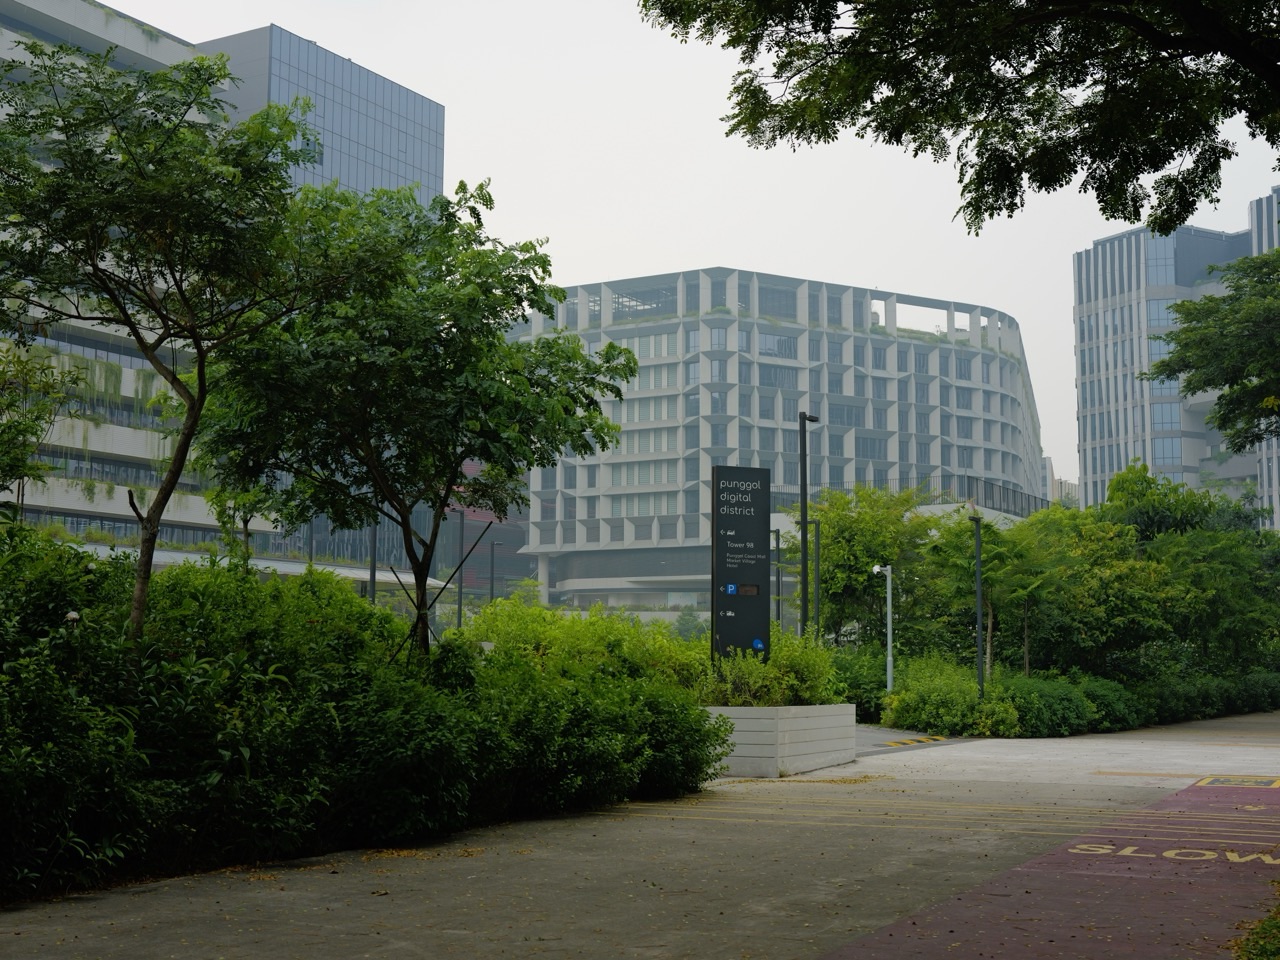
Punggol Digital District is becoming a visible technology location for Singapore’s banking industry, but that does not mean every financial-technology idea needs its own bank or payment licence. The most practical business opportunity for a Punggol, Sengkang or Pasir Ris entrepreneur between 2027 and 2037 may be to sell a carefully scoped service to an existing financial institution: secure reconciliation software, trustworthy data-quality tools, model-risk documentation, transaction monitoring support, compliance workflow design or reliable technology integration. The first commercial question is whether the company handles regulated financial activity or merely provides technology to someone who does. That distinction changes the permissions, costs, buyers and liabilities.
As at 1 November 2026, JTC identifies UOB and OCBC among Punggol Digital District’s financial-sector participants. In May 2026 UOB announced that it had begun moving approximately 3,000 technology and innovation staff into its purpose-built Tower 80 facility. The Monetary Authority of Singapore also published its Guidelines on Artificial Intelligence Risk Management for Financial Institutions on 7 October 2026, with staged effect from October 2027 and October 2028. MAS separately publishes Payment Services Act licensing information and anti-money-laundering requirements. These are established facts and dated regulatory developments—not guarantees of procurement contracts, startup revenue or banking jobs in Punggol through 2037.
- Industry: Digital banking technology, financial operations, RegTech, payment-service infrastructure and properly governed financial AI.
- Local anchor: Punggol Digital District’s banking and technology ecosystem, including UOB and OCBC.
- Potential buyers: Banks, appropriately licensed payment institutions, insurers, fintech companies and established financial technology vendors.
- Commercial roles: Technology supplier, data-processing contractor, software provider or—only with the required authorisation—regulated financial service operator.
- Current regulation: MAS rules vary by the actual business activity; the Payment Services Act does not make every ordinary software vendor a payment institution.
- AI timeline: MAS financial-institution AI risk guidelines take effect in stages from 7 October 2027 and 7 October 2028.
- Business risks: Data confidentiality, model errors, outsourced dependencies, cybersecurity, procurement complexity and long qualification periods.
- 2027–2037 principle: Forecasts are scenarios; named bank occupancy does not mean every startup can sell directly to a bank.

Why banking activity in Punggol matters to the wider business economy
A bank’s technology operation involves more than the app that a customer opens on a phone. Software teams build transaction systems, evaluate risk, test changes, monitor fraud and maintain services that must remain available when people need them. Large financial institutions also purchase support from external companies. That creates a wider value chain of technology providers, specialist testing firms, compliance advisers and carefully controlled service partners. A region containing a substantial banking technology workforce has an interesting skills and business network, even though actual vendor contracts may be bought through national or regional procurement offices.
The location matters most when it helps talented people collaborate, universities exchange ideas with companies, or suppliers understand complex customer problems. It matters much less when founders mistake an office move for an open purchasing programme. A bank can occupy Tower 80 and still have global supplier agreements that a small local firm cannot bypass. The opportunity begins with the problem, buying authority and required evidence—not the physical distance from a bank tower.
What UOB’s 2026 move actually established
JTC’s 5 May 2026 article reports UOB’s move of around 3,000 technology and innovation staff into Punggol Digital District. The bank described its approximately S$500 million facility as a hub for building and scaling banking capabilities. This is a meaningful industrial anchor. It is not evidence that a specific Punggol startup has signed a contract, that every person will be in the office every day or that an equal number of new external services must be purchased locally.
A supplier should ask what the bank actually procures from outside companies. Core technology decisions may remain in-house; specialist vendors may need enterprise-wide security approval; and some contracting may occur through regional arrangements. A firm with a useful product should research legitimate vendor processes and identify an appropriate sponsor for evaluation. The announcement can justify market research, but it cannot justify booking revenue in the startup’s financial forecast.
The difference between FinTech and RegTech
FinTech is a broad term for using technology in financial products and operations. RegTech refers to technology that helps organisations meet regulatory, supervisory, reporting or risk-management requirements. A payment app, a bank’s transaction reconciliation system, an automated compliance evidence register and a financial data-processing service may all use software, but they serve different buyers and involve different rules.
Some founders want to call every business involving financial data a fintech company. That label is not harmful by itself, but it conceals the practical problem. A regulator may examine the activities performed, not the entrepreneur’s preferred description. Selling an internal dashboard to an authorised bank is not the same as accepting deposits or operating a payment service. The company should map exactly what happens to money, instructions, customer data and decisions before writing its product brochure.
A software supplier does not automatically become a licensed bank
Suppose a business builds a system that matches a merchant’s invoices against payments already received through an authorised provider. If it only supplies software and does not itself carry on a regulated payment activity, its legal position may differ substantially from a company that receives and transmits customers’ money. Other obligations can still arise from data protection, cybersecurity, contracts and the precise service offered. A founder should not assume an exemption without checking the complete workflow.
The proper assessment starts with the money flow. Who holds funds? Who instructs transfers? Who contracts with the payer? Who issues e-money or provides the regulated payment service, if any? A developer that answers these questions early can avoid accidentally building a business model that needs costly licensing or changes to its operations. When the facts are unclear, competent regulatory advice is more useful than a generic claim that technology businesses do not need licences.
The Payment Services Act has defined categories and requirements
MAS explains that Singapore regulates specified payment services through categories that include money-changing and payment services covered by standard or major payment institution licensing. Which licence applies depends on the actual activity, transaction scale and statutory criteria. MAS publishes thresholds and requirements on its payment service provider licensing page. A startup should refer to that current official page and its legal advisers rather than rely on an old internet summary.
The commercial implications can be substantial. Fit-and-proper considerations, compliance resources, security, audit arrangements and technology risk management may be relevant to a licensed payment operator. A team that cannot fund those obligations should not promote itself as ready to launch a regulated national payment network. A more viable route might be supplying an approved technology component to an established institution under a clearly bounded contract.
Reconciliation is a useful example of a less glamorous problem
Imagine a merchant receiving payments from multiple authorised channels. Someone needs to match the orders, settlements, refunds, fees and bank records. When the numbers do not agree, staff spend time investigating. A software company may help organise these records and highlight exceptions. The immediate buyer benefit is not an advanced AI demonstration: it is fewer mistakes and faster identification of items requiring legitimate human review.
A credible reconciliation tool should preserve original records, identify duplicate entries, expose unexplained differences and keep a clear audit trail. It must not invent missing transactions to make totals match. A customer’s accounting staff should be able to see how each figure was calculated. A useful product starts with sample transactions and proves accuracy before seeking access to sensitive live financial information.
Anti-money-laundering technology serves people responsible for decisions
MAS describes risk assessment, customer due diligence, account review, monitoring, reporting and record keeping among the controls applicable to relevant financial institutions. A technology supplier may help authorised teams organise information or investigate patterns. It does not thereby become the regulator or take over all legal responsibility for a customer’s AML obligations.
Consider a tool that prioritises alerts for analysts. It must explain how alerts are generated and which inputs are reliable. An alert is not proof that a person committed a crime. The business should avoid language that labels customers as criminals based on a speculative model score. Its product should support lawful, accountable review and protect sensitive data. False positives, missed events, explanation quality and operational workload all matter to the buyer.
Customer due diligence is not only scanning an identity document
A vendor may advertise a quick identity check as the answer to financial compliance. But due diligence can include understanding relevant parties, beneficial ownership, risk, monitoring and the regulatory context. A document-reading service may support one part of that process without completing the institution’s entire responsibility. A responsible supplier describes this boundary clearly.
The buyer should ask how information is validated, where it comes from, who can correct errors and how the product handles uncertain records. Data minimisation is important, because collecting more sensitive information than necessary increases exposure without necessarily improving compliance. Strong documentation of assumptions and exceptions can be as valuable as sophisticated recognition technology.
The 7 October 2026 MAS AI guidelines change the planning calendar
MAS issued Guidelines on Artificial Intelligence Risk Management for Financial Institutions on 7 October 2026. They will take effect in stages: sections dealing with overarching governance and risk management from 7 October 2027, and further requirements from 7 October 2028, according to MAS’s announcement. The guidelines apply across financial institutions using AI, with proportionate expectations based on exposure and use. This is a real regulatory timeline that a potential RegTech supplier can understand.
A founder should not interpret the timeline as an automatic government procurement programme. Financial institutions remain responsible for their AI and may address the requirements internally. A vendor can propose a useful tool only after understanding the buyer’s existing frameworks, model inventory and gaps. The commercial opportunity lies in credible assistance with a concrete governance need, not in claiming that MAS requires every bank to purchase a particular software subscription.
AI inventories are an operational product category
An institution may deploy AI in customer service, fraud review, coding, risk analysis and ordinary office productivity. It needs to understand which systems are in use and what their material risks are. A product that maintains a useful AI inventory can help teams identify owners, purposes, changes, providers and controls. The challenge is that inventories become stale unless integrated with real workflows.
A startup might build a limited, auditable register for authorised staff. It should make the owner of each use case explicit and distinguish a proposed experiment from a live service. It can track approval and review dates without asserting that every registered model is safe. Buyers will evaluate accuracy, usability, security and the ability to export records. A simple reliable register may be more commercially useful than an elaborate display of model scores.
Third-party AI assurance is a difficult but real buyer problem
MAS’s October 2026 statement explains that financial institutions remain accountable for AI they use, even when it is developed or operated by third parties. They should obtain sufficient assurance and apply appropriate controls, limiting or replacing a service when risks cannot be managed. This principle creates due-diligence questions for vendors. Can they explain the model’s intended use, limitations, data handling and changes? Can they provide evidence of testing and incidents?
A supplier promising that its AI requires no customer oversight misunderstands the regulatory direction. A more credible contract includes documented responsibilities, change notices, evaluation results and mechanisms for termination or suspension. The vendor may need to make its service understandable to legal, risk, technology and operational teams simultaneously. Commercial maturity includes accepting scrutiny as part of the sale.
Human oversight must mean a real operating process
A vendor may claim that its AI remains human-in-the-loop. That phrase is insufficient unless the institution knows which decisions a person reviews, how uncertainty is displayed and what authority the reviewer retains. If a system automatically proposes an account restriction or compliance escalation, the buyer needs to understand the consequences of an error and the permitted response.
A product team should document thresholds, escalation steps and how users can challenge or correct the output. It should provide a way to inspect the underlying facts without exposing confidential information unnecessarily. Testing should include difficult cases and not just an ideal demonstration. Buyers may reasonably refuse to use an apparently accurate model if staff cannot understand when to trust it or how to stop it.
Technology risk management is a separate purchasing requirement
Financial technology must operate securely and reliably. A vendor may be asked about system availability, vulnerability management, access controls, incident reporting, encryption, backup and recovery arrangements. MAS publishes technology risk management guidance, and individual institutions can impose stronger contract conditions. A developer who focuses only on features may underestimate the work necessary to become an approved supplier.
The prudent company prepares a security and operations pack before enterprise sales. It identifies where data is stored, which subcontractors support the service, the disaster-recovery approach and how customer access ends. It can explain what happens during an outage. Claims should be backed by tests and current documentation, not by a certificate logo borrowed from a cloud provider. A strong operational design can make a small vendor more credible.
Outsourcing does not transfer the bank’s accountability
When a financial institution uses an external technology supplier, it remains responsible for managing the associated risks. MAS’s outsourcing and third-party risk framework reinforces the need for governance and appropriate oversight. The vendor should expect due diligence and continuing review. A bank may ask how the service would be transitioned to another provider if necessary.
A startup may find this inconvenient, but it is normal in a high-trust industry. A clean exit plan, secure data export and documented responsibilities help the customer make a buying decision. Proprietary lock-in that prevents an institution from retrieving its own information can be a commercial weakness. A vendor that offers transparent service boundaries and orderly handover may win trust without being the cheapest choice.
Data confidentiality shapes architecture from the beginning
Financial records can be sensitive even when the software is described as internal reporting. Customer names, transaction histories, account details and security logs should never be copied casually into an external demonstration environment. A supplier should begin with synthetic data where possible, request only the data necessary for the authorised purpose and establish appropriate retention and access controls.
The design must consider different client institutions. A multi-tenant SaaS product should prevent one client’s information from appearing in another client’s records. Staff access must be restricted and audited. A contract should explain whether any data is used to improve the vendor’s models. Silence is not a suitable substitute for permission. Strong privacy engineering is a product capability rather than legal paperwork added after the application has been built.
The bank’s procurement team is not the product champion
A technology manager may admire a prototype, but an enterprise purchase can involve compliance, risk, cybersecurity, finance, procurement and legal departments. The person who wants the product may not have the authority to buy it. Founders should identify those decision makers and their concerns early instead of treating a positive first meeting as a confirmed contract.
A procurement-ready proposal includes scope, pricing, technical architecture, relevant assurances, service levels, data handling, business continuity and a realistic deployment plan. It should also state exclusions. A vendor that cannot disclose the required information may need to mature its operations before pursuing a major bank. The next useful step may be a smaller paid customer, not an elaborate presentation to a prominent institution.
A bank’s presence is not a grant of PDD access
The wider Punggol Digital District includes a university, technology companies and testbed concepts, but not every part of it is publicly available for commercial experimentation. A bank’s protected systems and premises remain under its own access and security rules. A founder cannot scan networks, interview employees about confidential projects or request operational data without appropriate authorisation.
The legitimate path is an approved collaboration or vendor engagement. A company can prepare a convincing product using synthetic examples, then seek formal review. The strongest local ecosystem is one in which innovation respects property, privacy and trust. Treating a district as an open hacking playground would undermine the very business opportunities that make it interesting.
A small RegTech company’s first product
Consider a fictional startup whose founders know how difficult it is to maintain policy-change records. It creates an application that tracks the owner, current status and approval history of internal compliance tasks. The product does not interpret all law automatically or make binding regulatory decisions. It helps the customer’s qualified staff find the right documents and see which actions are overdue.
The startup tests the software with invented cases and asks potential buyers which reports they actually need. It then measures reduced administrative time and error frequency in a permitted trial. If the customer finds the tool useful, the company can improve integrations and controls. The first product succeeds by supporting a defined workflow rather than claiming to automate the compliance department.
A fictional payment reconciliation supplier
A second startup provides matching software to a licensed payment institution. The institution retains the regulated payment functions, while the startup processes authorised settlement records under a contract. The vendor needs secure storage and an accurate reconciliation method. It defines what happens when records cannot be matched and who can approve adjustments.
The buyer might value a reduction in manual exception handling. To establish this, both parties agree on a baseline of working hours, accuracy and outstanding cases. If the software flags more false exceptions than it resolves, the trial may be unhelpful. The supplier should report this honestly rather than claim a favourable outcome by selecting only easy transactions. Accurate financial records matter more than an impressive dashboard.
A fictional financial AI model registry
An enterprise customer wants better oversight of internal AI systems before MAS’s staged 2027–2028 expectations take effect. A software vendor proposes an authorised inventory, classification and evidence register. It ensures that every model has an accountable owner, intended use and review method. It does not decide the customer’s regulatory compliance automatically.
The commercial value is easier audit preparation and better communication among technology, risk and business teams. The system must remain current when models change and when a third-party provider releases an update. A successful pilot may still require a great deal of organisational work. A software purchase cannot replace governance, but it can make governance easier to carry out.
Enterprise licensing requires realistic support commitments
A software company may be tempted to charge a large annual subscription and assume its costs will remain low. Financial institutions may require security review, integration, incident support, service documentation and regular assurance. Those obligations can consume substantial staff time. A contract with a relatively high value may still have a weak margin if every new customer requires expensive custom development.
The founder should separate standard product features from customer-specific work. It should price implementation, ongoing support and approved changes transparently. A simple service-level agreement can clarify availability, support hours and escalation. The goal is to build a repeatable business, not a portfolio of expensive one-off projects disguised as software subscriptions.
Illustrative RegTech unit economics
Suppose a fictional SaaS supplier earns S$12,000 per month from a bank for an approved internal reporting tool. Its allocated secure hosting and licence costs are S$2,000, technical support is S$3,500 and compliance or assurance work averages S$1,500. Before other staff, sales and corporate overhead, the contribution is S$5,000 monthly. These are teaching figures, not quoted prices from UOB, OCBC or another institution.
If the customer requires three additional full-time engineers and a unique platform integration, the economics could change entirely. A startup should examine contribution after direct service costs, not merely the headline contract. It should also consider the time to obtain the contract and the possibility of a delayed renewal. A product that is easy to sell to one bank but costly to support across others may not scale as expected.
A cost model for payment services is different
A regulated payment business may face compliance, capital, audit, technology and operational obligations that do not apply in the same way to a simple software vendor. Transaction volumes, customer funds and service categories matter. MAS’s licensing information describes specific thresholds and criteria. A founder should model the cost of the intended regulated activity with suitable professional advice before claiming that a modest software team can become a large-scale payment operator immediately.
The company must also consider consumer complaints, fraud response, continuity, settlement arrangements and the credibility of its funding. A business with fast transaction growth can still struggle if compliance and support do not grow appropriately. When necessary, it can work with an authorised provider instead of trying to take on every financial obligation itself.
Selling to SMEs rather than banks
A fintech or RegTech supplier might find its first buyers among ordinary SMEs needing clearer invoicing, reconciliations or authorised risk reporting. This can reduce some enterprise procurement obstacles, although customers still expect security and truthful claims. The product should be designed for the buyer’s actual skills, budget and work process rather than repackage a bank-scale platform into a small shop.
For a Punggol retailer, the value may be correct settlement information and fewer hours spent resolving refunds. The founder should demonstrate the result with real consent and appropriate data. A product can be commercially useful without collecting payment funds itself. Small customer success can create credible references, subject to permission, before the company pursues more complex institutional contracts.
Competitive advantage is evidence, not the word AI
Many vendors now describe their products as AI-powered. Financial buyers are likely to care about outcomes, robustness, interpretability and support more than the label. A tool with reliable rules and accurate records may outperform a generative model in a narrowly defined compliance workflow. The founder should choose technology according to the task and risk, not publicity.
A credible evaluation compares the product with the current method. It records accuracy, time saved, failure modes and the effect on people who must review results. The vendor should disclose what it has measured and what remains uncertain. These habits matter even more when a wrong result can affect a customer’s financial position or reputation.
Financial fraud and consumer trust
A company that deals with financial data or fraud detection must avoid implying that every suspicious transaction is confirmed misconduct. False positives can inconvenience innocent customers, while missed events can expose people to losses. A product should support appropriate verification, review and appeal channels according to the customer’s regulatory obligations. It must be careful not to create unfair or unexplained decisions.
The supplier should treat consumer trust as part of the outcome. A tool that saves staff time but causes unjustified blocks or exposes information may be a poor product. The financial institution is the regulated party in many arrangements, but a responsible vendor can help it meet obligations through reliable design and clear records.
Punggol talent and SIT collaboration need formal agreements
SIT’s campus in Punggol creates an applied-learning environment where technology firms may wish to work with graduates or research teams. A startup can benefit from skills in software engineering, data analysis and business design, but a project must have appropriate agreements. Student involvement does not automatically give a company ownership of research outputs, and a university logo should not be used as a commercial endorsement without permission.
A defined collaboration might test a synthetic-data prototype or study human oversight in a workflow. The team should clarify confidentiality, data use, supervision and intellectual-property ownership. Production financial software needs additional enterprise assurance before deployment. Treating education, research and customer operation as distinct stages protects everyone involved.
2027–2029: governance creates a concrete timeline
The near-term period includes the staged MAS financial-institution AI risk guideline effect dates in October 2027 and October 2028. Organisations may develop internal governance and review vendor systems during this period. A supplier that builds useful tools may find customers, but should not assume the legal timetable guarantees new purchases or a set market size.
A practical business plan starts with a well-defined product, authentic customer interviews and a controlled pilot. It budgets for procurement and security checks that may take longer than expected. A founder should aim to earn revenue from a real need while preserving cash. The milestone is a trustworthy product that works, not merely adding the regulatory year to a sales pitch.
2030–2033: operational reliability becomes the differentiator
Once financial institutions have established stronger governance practices, vendors may face continuing expectations around monitoring, updates, third-party assurance and records. That can create demand for ongoing tools and support, but it also makes customer retention dependent on reliable service. A company may need more security and operations staff even as software development becomes faster.
The founder should review whether the product can support multiple customers without bespoke work overwhelming the team. Clear interfaces, standardised documentation and a reliable exit process help. The business may specialise in one niche—reconciliation, AI governance or vendor-risk evidence—rather than try to become a full banking platform.
2034–2037: plan for changing technology and regulation
A decade is long enough for today’s AI systems, payment services, risk practices and customer preferences to change. A product tied to one model provider or bank interface may become obsolete. A resilient software supplier retains the ability to migrate data, update controls and explain its service to customers who face new obligations. It also has contracts that address replacement and orderly termination.
The goal is not to predict the exact RegTech market in 2037. It is to build an organisation that can repeatedly solve real problems without compromising confidential information or overstating regulatory status. Banks and consumers ultimately need trustworthy operations. Vendors that keep this in view have a stronger foundation than firms built on one fashionable technology.
Practical questions before selling financial technology
- Who is the paying customer and who has purchasing authority?
- Is the company only a technology supplier, or does it perform a regulated financial service?
- What actual money flows, records and decisions does the product affect?
- Which MAS laws, notices or guidelines apply to the exact business arrangement?
- What data is required, where will it be stored and who may access it?
- Is a synthetic-data pilot sufficient for early testing?
- How will the buyer assess accuracy, security and failure modes?
- Can the system explain uncertain AI or compliance results to a qualified reviewer?
- What happens when a third-party model or cloud service changes?
- Who responds during outages and security incidents?
- Are integration, audit and support costs priced honestly?
- What evidence supports claimed savings and commercial readiness?
- Can the customer retrieve records and end the contract safely?
- What happens if an enterprise procurement cycle takes twice as long as expected?
These questions distinguish a product roadmap from an operating enterprise. A firm can begin with one narrow tool and a small customer base, then build credibility. There is no advantage in claiming to operate a bank when the actual expertise lies in improving a valuable workflow.
Frequently asked questions
Does every FinTech startup need an MAS payment institution licence?
No. Requirements depend on the actual regulated activity. A supplier that only develops software may be different from a business providing a regulated payment service. The precise facts and current MAS rules must be checked before operating.
Are UOB and OCBC part of Punggol Digital District’s ecosystem?
JTC’s business page lists both institutions, and UOB announced its Tower 80 move in May 2026. This does not mean either institution endorses a particular vendor or offers open contracts to all nearby businesses.
Are MAS’s October 2026 AI guidelines already fully in force?
No. MAS published them on 7 October 2026 and set staged effect dates for 7 October 2027 and 7 October 2028. Financial institutions should review the precise staged provisions; suppliers should not misstate the timetable.
Can AI take over every compliance decision automatically?
A business should not make that claim. MAS emphasises accountable governance, proportional controls and management of third-party AI risks. The suitability of automation depends on the actual task and risk.
Does having more AI models prove a bank is more innovative?
No. The value lies in safe, useful outcomes. A carefully controlled process can be more valuable than dozens of untested models. A vendor should show evidence that its service improves an authorised business function.
Will FinTech activity in Punggol guarantee startup profits until 2037?
No. Market demand, licensing, procurement, competition, security and execution all affect outcomes. The 2027–2037 window is a planning horizon, not an official revenue projection.
Your Next Step: a buyer, a bounded workflow and a credible pilot
Choose a concrete financial operation that needs improvement, such as reconciliation or an authorised compliance evidence register. Identify the customer, who can approve the project and whether the activity requires MAS authorisation. Build a synthetic-data prototype that makes its method and limits visible. Calculate total implementation and support costs, then seek a properly scoped trial. In financial technology, a trustworthy small improvement can be worth more than an ambitious unsupported claim.
Official sources and further reading: JTC’s Punggol Digital District business ecosystem, JTC’s 5 May 2026 UOB Tower 80 announcement, MAS’s 7 October 2026 AI risk guidelines announcement, MAS financial-institution AI guidelines, MAS payment-service provider licensing and MAS anti-money-laundering requirements. Verify regulatory conditions and commercial arrangements before taking action.


